

Policies & IssuesOct 06, 2026
6 Charged in Connection to String of New Jersey Smash-and-GrabsThe alleged thieves used crow bars and sledgehammers to smash into jewelry stores across the state.



With the recent data breaches impacting major retailers and web security issues stemming from Heartbleed, National Jeweler takes a look at what jewelers can do to protect their customers.


New York--The past six months have been rough for the security of private consumer information.
Target and Neiman Marcus both fell victim to massive data breaches, leaving millions of customers vulnerable. The web world was thrown into further turmoil with news of a massive security flaw in OpenSSL, the security software used on about two-thirds of all servers on the Internet.
Though no cases have yet been reported of the flaw, which is called the Heartbleed bug, being used to obtain information, its potential reach is troubling, allowing for the removal of personal and financial information without anyone’s knowledge.
Retailers are responsible, from many standpoints, for making sure they’re doing everything they can to protect this information.
National Jeweler talked to a number of security experts--Matt Boaman of EZSolution, James Koons of Listrak, Chris Kronenthal of FreedomPay, Andrew Van Noy of Warp 9, Aaron Janowski of Wellsley Consulting and consultant to the Jewelers’ Security Alliance, and Zilvinas Bareisis of Celent--to compile the following list of tips for retailers to secure their customers’ information.
1. Monitor the information. The Heartbleed bug is invisible, so no one can establish ahead of time what information has already been compromised; instead, jewelers should be monitoring for any signs that it has been. The monitoring and response plan is key to being able to show that the company is taking all reasonable steps to keep secure the personal data that is processed.
2. Test the site. This site provides a place to plug in URLs to check if a website is vulnerable to the Heartbleed flaw.
3. Fix the problem. Contact the web host to ensure that if the web server was running one of the vulnerable versions of OpenSSL, they have updated it or patched it right away. Once that’s finished, get a new key for the site’s security certificate.
4. Communicate with customers. Advise customers not to log into the site until it’s been fixed. Once it has, tell them to reset their user passwords if they have an account through the website. They shouldn’t do so before it’s been fixed as that could open them up to more vulnerability.
5. Don’t store unnecessary information. Don’t keep any unnecessary information on a server that doesn’t need to be there. Instead, encrypt the information before sending to a credit card processor.
6. Plan ahead. Consider getting involved in organizations like the Online Trust Alliance, which advocates
Data breaches also continue to be top of mind, as companies work to make sure they’ve secured their payment systems after millions of customers’ information was stolen from Target and Neiman Marcus. Target recently named a new chief information officer and security updates to show consumers it’s taking steps to protect them.
RELATED CONTENT: Target hires new CIO, announces security updates
These breaches can have numerous negative effects for a retailer.
“Whether the result of an online attack, in-store breach, internal theft, malware or accidental loss of data incident such incidents can have significant financial impact and can have devastating consequences on the value of a company’s brand,” said Koons, who is chief privacy officer at Listrak.
The National Retail Federation has since been urging Congress to overhaul the nation’s credit and debit card system, saying that banks’ insistence on a signature instead of a personal identification number, or PIN, puts customers at risk. The organization is also urging the card industry to switch to new chip-and-PIN cards, much as Target is doing now, which would require use of a PIN instead of the signature.
There are a number of steps that jewelers can take to prevent a data breach.
1. Check the connection. Make sure that the merchant account with the banks being used to process sales is secure.
2. Check the equipment. Ensure the in-store equipment is loaded with anti-hacking, anti-virus software and/or hardware so that nothing on premises is corrupted, which is usually done by proper firewalls, data encryption and security hardware.
3. Do a double take. Double check with the credit card holder's bank for the validity and security of the credit account being used.
4. Prepare for the possibility. Security threats will always be a possibility, and businesses can’t wait until after it happens to figure out what to do. It’s necessary to have a plan to deal with security breaches and other incidents should it happen.
5. Explore all options. There isn’t one technology that will give all the protection needed against cybercrime. Follow a “layered approach” to security and use a number of tactics, including using EMV, tokenization, point-to-point encryption, and dynamic authentication, among other things.
6. Stay up-to-date. Make sure antivirus and operating systems are up to date with the latest software updates to provide the best protection against threats.
7. Keep it off-site. Avoid storing data unless absolutely necessary. If it’s necessary, they should follow PCI Security Standards Council guidelines.
8. Be proactive. Ensure cashiers always check the customer’s identification and/or ask for the PIN.
If a data breach should occur, immediate action is necessary to help regain security, preserve evidence and protect the brand. Here are steps to follow within the first 24 hours:
9. Jot down activity. Record the date and time when the breach was discovered as well as the current date and time when the team was alerted to the breach.
10. Secure the site. If a data breach comes from inside the store, secure the premises where it occurred to preserve evidence.
11. Prevent more activity. Stop additional data loss by taking affected machines offline but do not turn them off or start investigating in the computer until professionals are there to help.
12. Take extensive notes. Document everything known about the breach so far, including who discovered it, who reported it, to whom was it reported, who else knows about it, what type of breach occurred, what was stolen, what systems are affected, what devices are missing and any other pertinent information.
13. Interview. Talk to the team members who found the breach and anyone else who may know about it and document it to get all the relevant information.
14. Get professional help. Bring in a forensics team to begin the in-depth investigation.
15. Contact law enforcement. If needed, notify law enforcement after consulting with legal counsel and the entire upper management team.

The alleged thieves used crow bars and sledgehammers to smash into jewelry stores across the state.

Ahead of the holidays, Smith urges jewelers to take a hard look at who’s buying jewelry, what they’re purchasing, and who’s stopped buying.

In the new consumer-facing campaign, four fashion and lifestyle creators share the stories behind their natural diamond pieces.
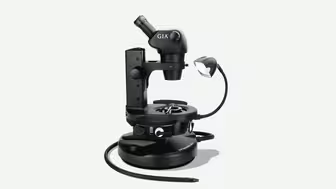
Experience gemstones with greater precision and comfort than ever before.


FGI President John Orrico is also leaving the company after more than 13 years.

The 2026 edition will feature presentations on alternative materials and design trends, as well as pop-up activations on the show floor.

It is the last fully operational diamond mine in Canada following the recent closures of Ekati and Diavik.
Submit your pieces for a chance to win in this year's competition.

These jewels stood out at Bonhams’ sale of the cat-loving tech entrepreneur’s collection of objects depicting the feline form.

The fine jewelry brand has expanded the collection that debuted at Couture with four new designs based on its most popular styles.

The AGTA president was elected for a two-year term on the board of directors.

The partnership, a pledge to protect Africa’s Okavango River Basin, has been extended for an additional five years.

The new facility, its first outside of Thailand, will boost its manufacturing capacity by 50 percent.

The special-edition “Dream” pendant, our Piece of the Week, was created to mark Hearts On Fire’s 30-year milestone with 30 diamonds.

Dubai Jewelers in Springfield, Virginia, was once again the target of an armed robbery.

YouGov’s 2026 U.S. Most Recommended Brands report’s out, and a fast-fashion giant is sitting at No. 1 while Rolex is just shy of the top 5.

Proceeds from its jewelry raffle will benefit an organization working in India to combat silicosis, a lung disease affecting stone cutters.

The rings, crafted by Jason of Beverly Hills, celebrate the hockey team’s Stanley Cup win with design elements that honor its traditions.

This roundup of birthstone jewelry for October features vibrant tourmalines and opals with personality.

President Duma Boko spoke at back-to-back events in the city last week, touting Botswana’s stability and the diamond “bounceback.”

The catalog showcases 112 new, one-of-a-kind pieces amid highlights from the jeweler’s historic archive.

Its Montepuez Ruby Mining operation in Mozambique, which is not yielding enough high-quality rubies, has taken a $125 million hit.

Those surveyed were worried about the present and the future, with write-in responses mentioning high oil and gas prices.

The event will take place on the evening of Oct. 26 in New York City.

She is remembered for her joie de vivre, upbeat personality, genuine interest in other people, and love of the Alabama Crimson Tide.
Online bidding is open now for Julien’s sale of items owned by the “Walk On By” singer, whose final album comes out this fall.

The founder and executive chairman of Stuller Inc. is being honored for his impact on the jewelry industry at the 25th annual Gem Awards.


This site uses cookies to give you the best online experience. By continuing to use & browse this site, we assume you agree to our Privacy Policy


